

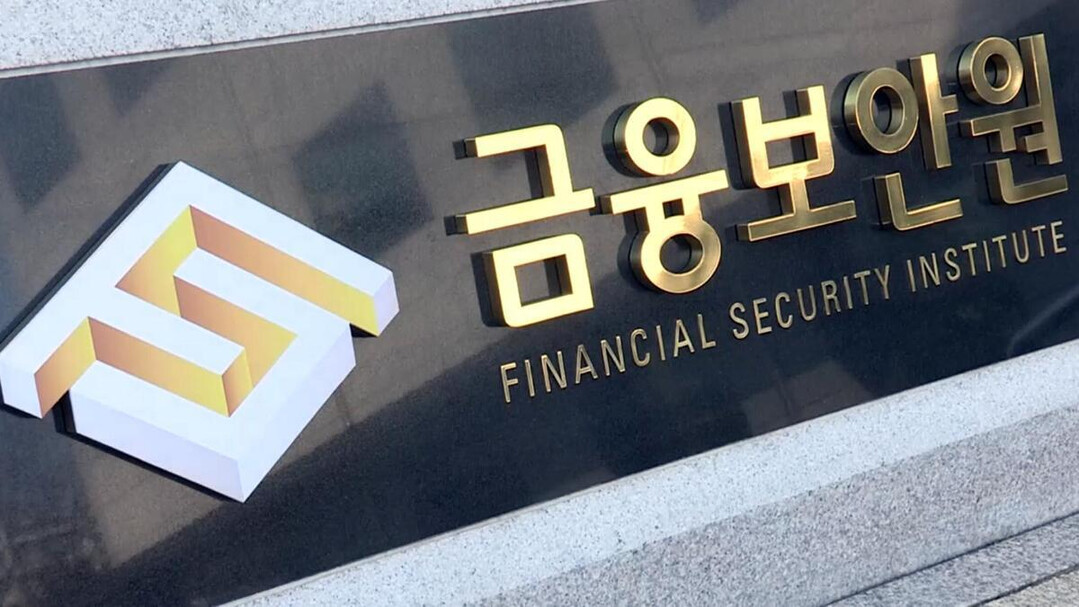
SEOUL — South Korea’s Financial Security Institute (FSI), the premier state-backed organization tasked with safeguarding the nation's financial cyber infrastructure, has suffered a data breach, compromising the contact information of hundreds of financial workers.
The security failure is a severe blow to the institution's reputation, occurring just days before it is set to host a major cybersecurity conference focusing on artificial intelligence governance and regulatory defense strategies.
According to financial regulators on Tuesday, the breach took place within the FSI's "Continuous Evaluation Support System"—a platform utilized to audit and assess the security compliance of financial institutions. Regulators were formally notified of the intrusion immediately after the breach was detected and containment protocols were activated.
Investigators revealed that the perpetrator employed a rotating IP address strategy, constantly shifting network locations with each request to masquerade as legitimate traffic. Although the attack methodology is not novel, the fluid IP rotation successfully bypassed the FSI’s automated monitoring filters, which mistakenly flagged the requests as routine user activity. The specific origins and nationalities of the offending IP addresses remain under investigation.
"Because the IP addresses changed continuously to mimic normal access, the activity slipped past our defenses," an FSI representative explained, noting that a static IP approach would have triggered immediate detection.
The compromised platform handles administrative documentation submitted by financial entities during routine security evaluations. While core financial networks and sensitive consumer data—such as bank account records or asset details—were reportedly untouched, the breach exposed secondary administrative data, including corporate email addresses and office telephone numbers of staff members managing compliance. Individual names on the files had been masked, and authorities are currently conducting a comprehensive audit to determine the exact scope of the leak.
"While highly sensitive identifiers like resident registration numbers and core security architectures were not compromised, the fact that an organization mandated with preventing cyberattacks has itself been breached is entirely unacceptable," an official from the Financial Services Commission (FSC) stated.
The FSI has begun issuing individual notifications to affected financial firms and pledged to compensate any member company employees who suffer secondary damages. Regulatory bodies have ordered a full forensic investigation into the incident to establish accountability and reinforce system vulnerabilities.
[Copyright (c) Global Economic Times. All Rights Reserved.]